Collect evidence once. Satisfy every framework you carry.
Run your entire internal compliance program in one place, so the evidence you collect once counts toward every framework you carry. Continuous control monitoring and an AI-assisted policy lifecycle, built to cut audit evidence work by up to 60% (illustrative target).
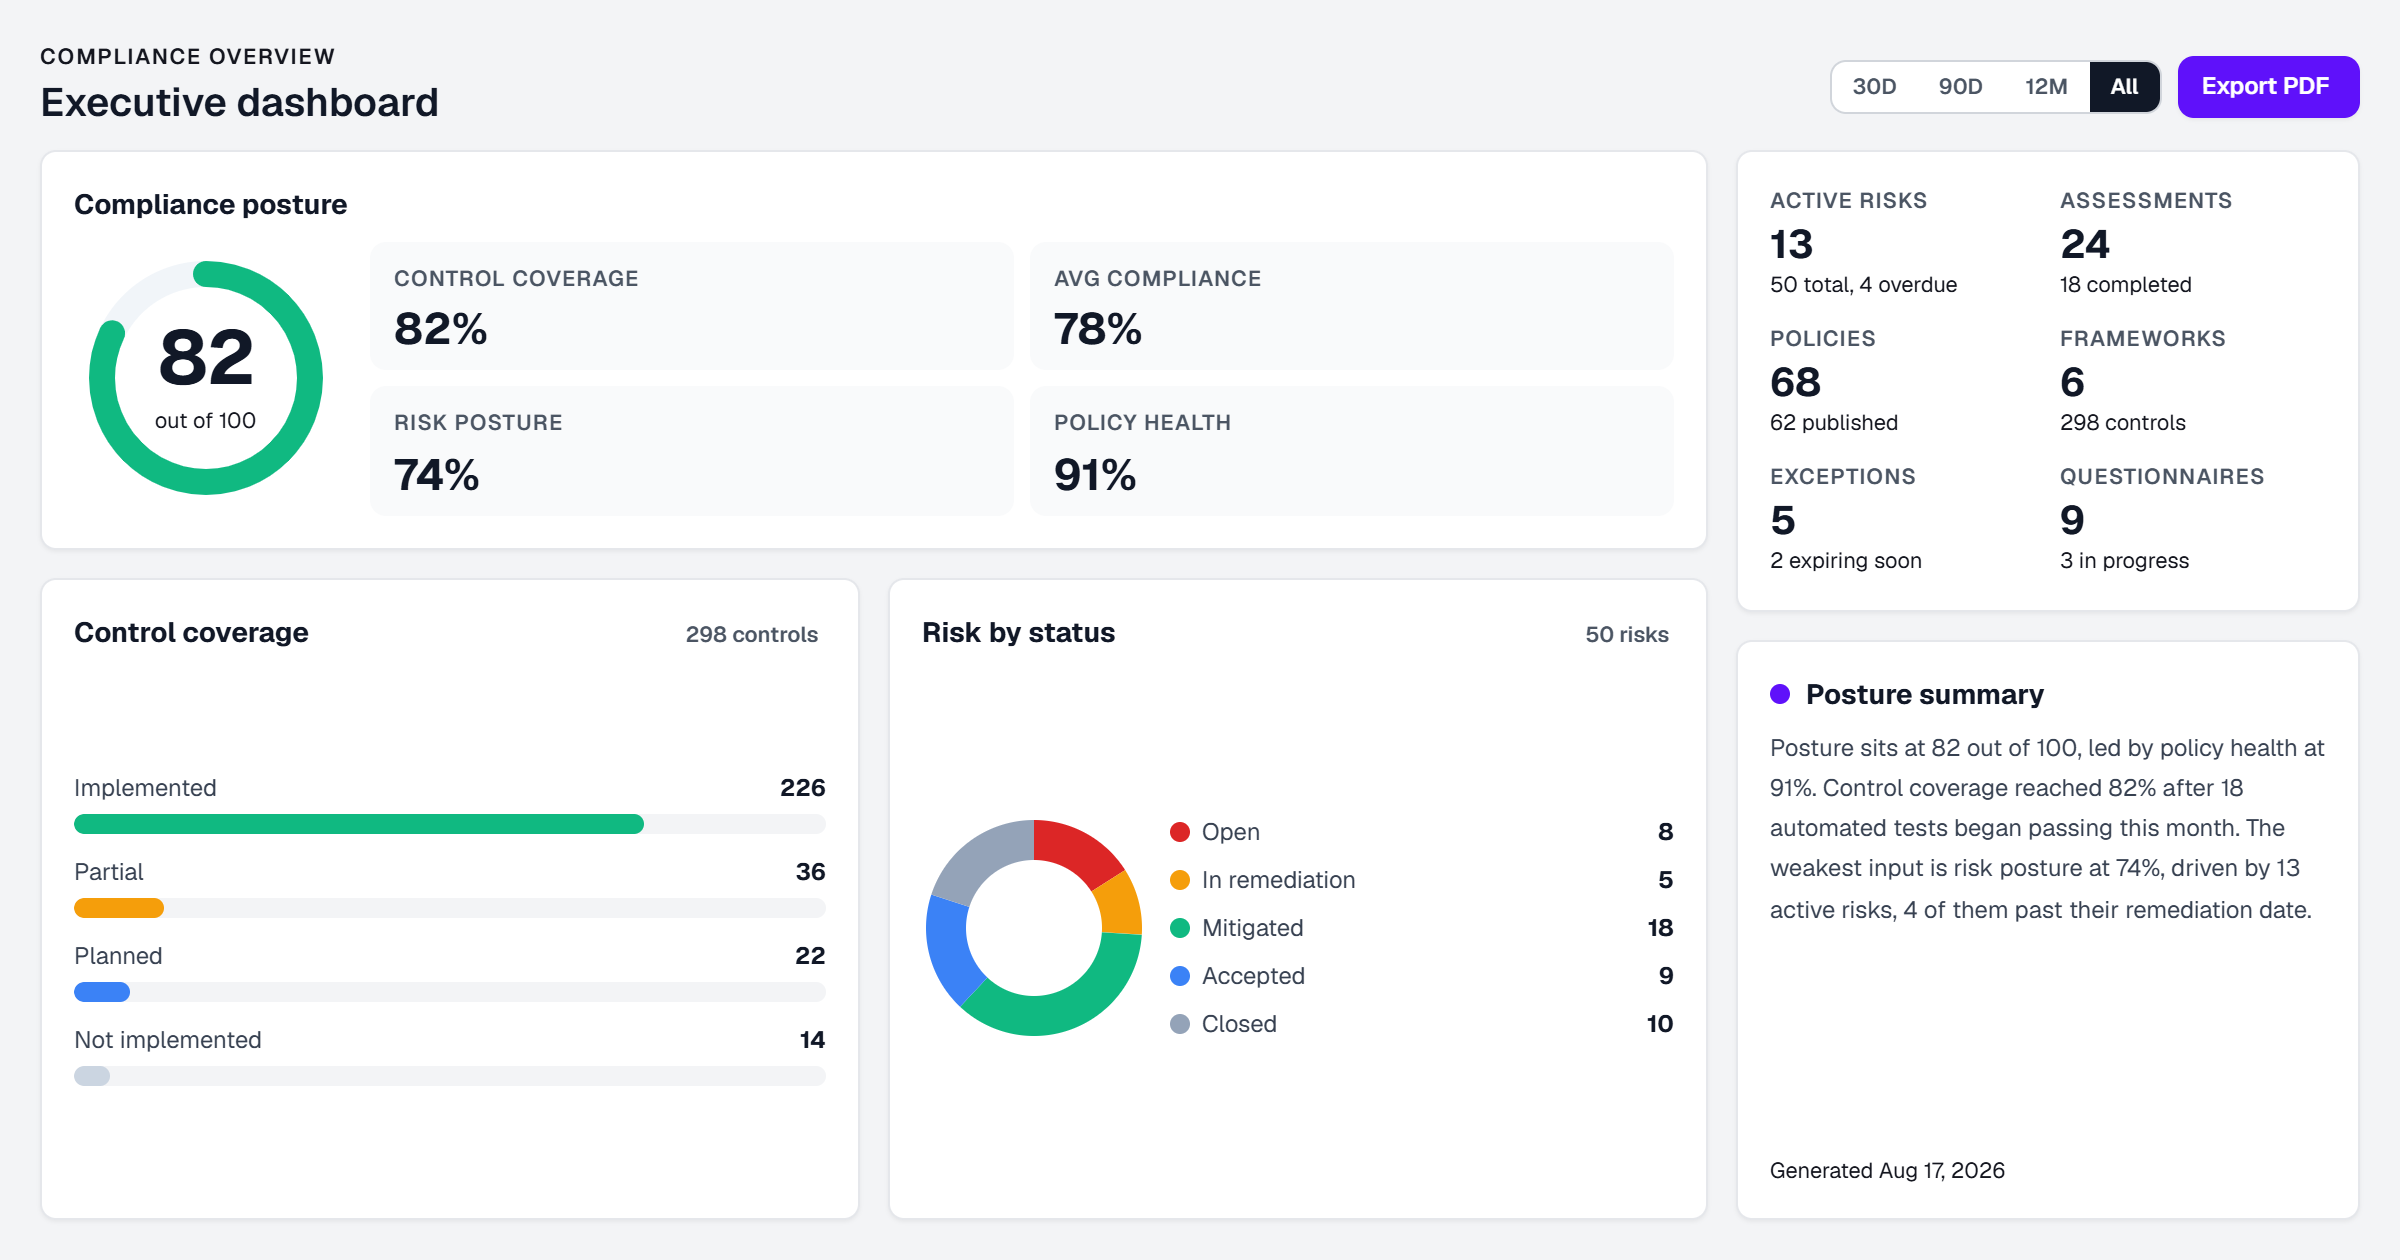
Everything an internal GRC program needs.
The major frameworks, ready out of the box
SOC 2, ISO 27001:2022, HIPAA, NIST 800-53 Rev 5, NYDFS Part 500, and more ship included. Add custom frameworks for sector-specific requirements, and collect evidence once to satisfy the overlap.
- Major frameworks included
- Cross-framework control mapping
- Custom framework support
Continuous control monitoring
The GRC Monitor Agent runs nightly health checks across control implementation, assessment SLAs, risk SLAs, policy currency, and evidence freshness, flagging drift before it shows up on a board report.
- 5-dimension nightly health score
- Anomaly detection on internal posture
- Delta notifications on degradation
AI-assisted policy lifecycle
Effy drafts policies aligned to your controls, flags coverage gaps, and routes through approval. PolicyVersion records become immutable on publish. Your auditor sees what was published, when, and by whom.
- AI policy drafting + gap detection
- Approval workflow built in
- Immutable PolicyVersion on publish
Three steps from setup to value.
Pick your frameworks
Activate any of the included frameworks (SOC 2, ISO, HIPAA, NIST, NYDFS, and more) or upload your own controls. Mappings auto-populate where overlaps exist.
Connect your evidence
Drop in your existing evidence: pen tests, certifications, screenshots. The vault indexes everything for AI retrieval and links artifacts to controls automatically.
Let Effy draft + monitor
Effy drafts policy gaps, runs nightly health checks, and surfaces anomalies. Your team reviews and approves, never AI on its own.
Everything above is recorded so it survives an examiner.
Published policy versions are immutable, evidence locks once it is attached to an approved assessment, nothing with audit significance is ever hard-deleted, and your auditor gets a read-only role enforced in the data layer rather than a UI toggle.
See how integrity is enforced- SOC 2
- ISO 27001
- NIST CSF 2.0
- NIST 800-53
- CIS v8.1
- PCI DSS
- HIPAA
- GDPR
- NYDFS 500
- NYSDOH 405.46
Every framework here runs on the same control set and the same evidence. Activate the ones you carry, and the overlap maps itself.